统一身份认证
所需要的java示例代码请自取: https://nas.wangyuxiang.vip/
账号: root
密码: wyx123..
测试申请信息
txt
应用编码(pid):11683
应用code/名称:中国石化广州石化炼油生产调度与优化管理系统
entityid:http://10.119.30.71/api_root
连接账号:gzsh_11683
队列标识:gzsh_11683
连接密码:单独反馈
应用账号管理员:zhouyj272
请结束智云流程,谢谢!
测试环境用户默认密码为pcitc@#2020,测试完成后请将测试报告反馈至tysf01@sinopec.com,测试报告下载地址:https://auth.uat.siam.sinopec.com/help/
因证书变更,测试示例请下载最新版本示例,uat环境统一身份控制台:https://idm.uat.siam.sinopec.com
提示:应用系统服务器与时间同步配置修改为与 time.sinopec.com 进行同步。
ps:该邮件为交付邮件,请勿回复。
帮助网站: https://auth.uat.siam.sinopec.com/help/集成的整个流程
- 测试
提交申请 --> 注册应用 --> 测试环境开始集成统一身份认证 --> 测试完毕 --> 写测试报告 --> 申请生产环境 - 生产
nginx配置https证书 --> 制作生产jks证书(java使用jks,其他语言使用p12) --> 改配置文件 --> 帮助网站加密证书密码(DES加密)、应用code,中文需要ASCII转码 --> 打包测试
需要用的网站:
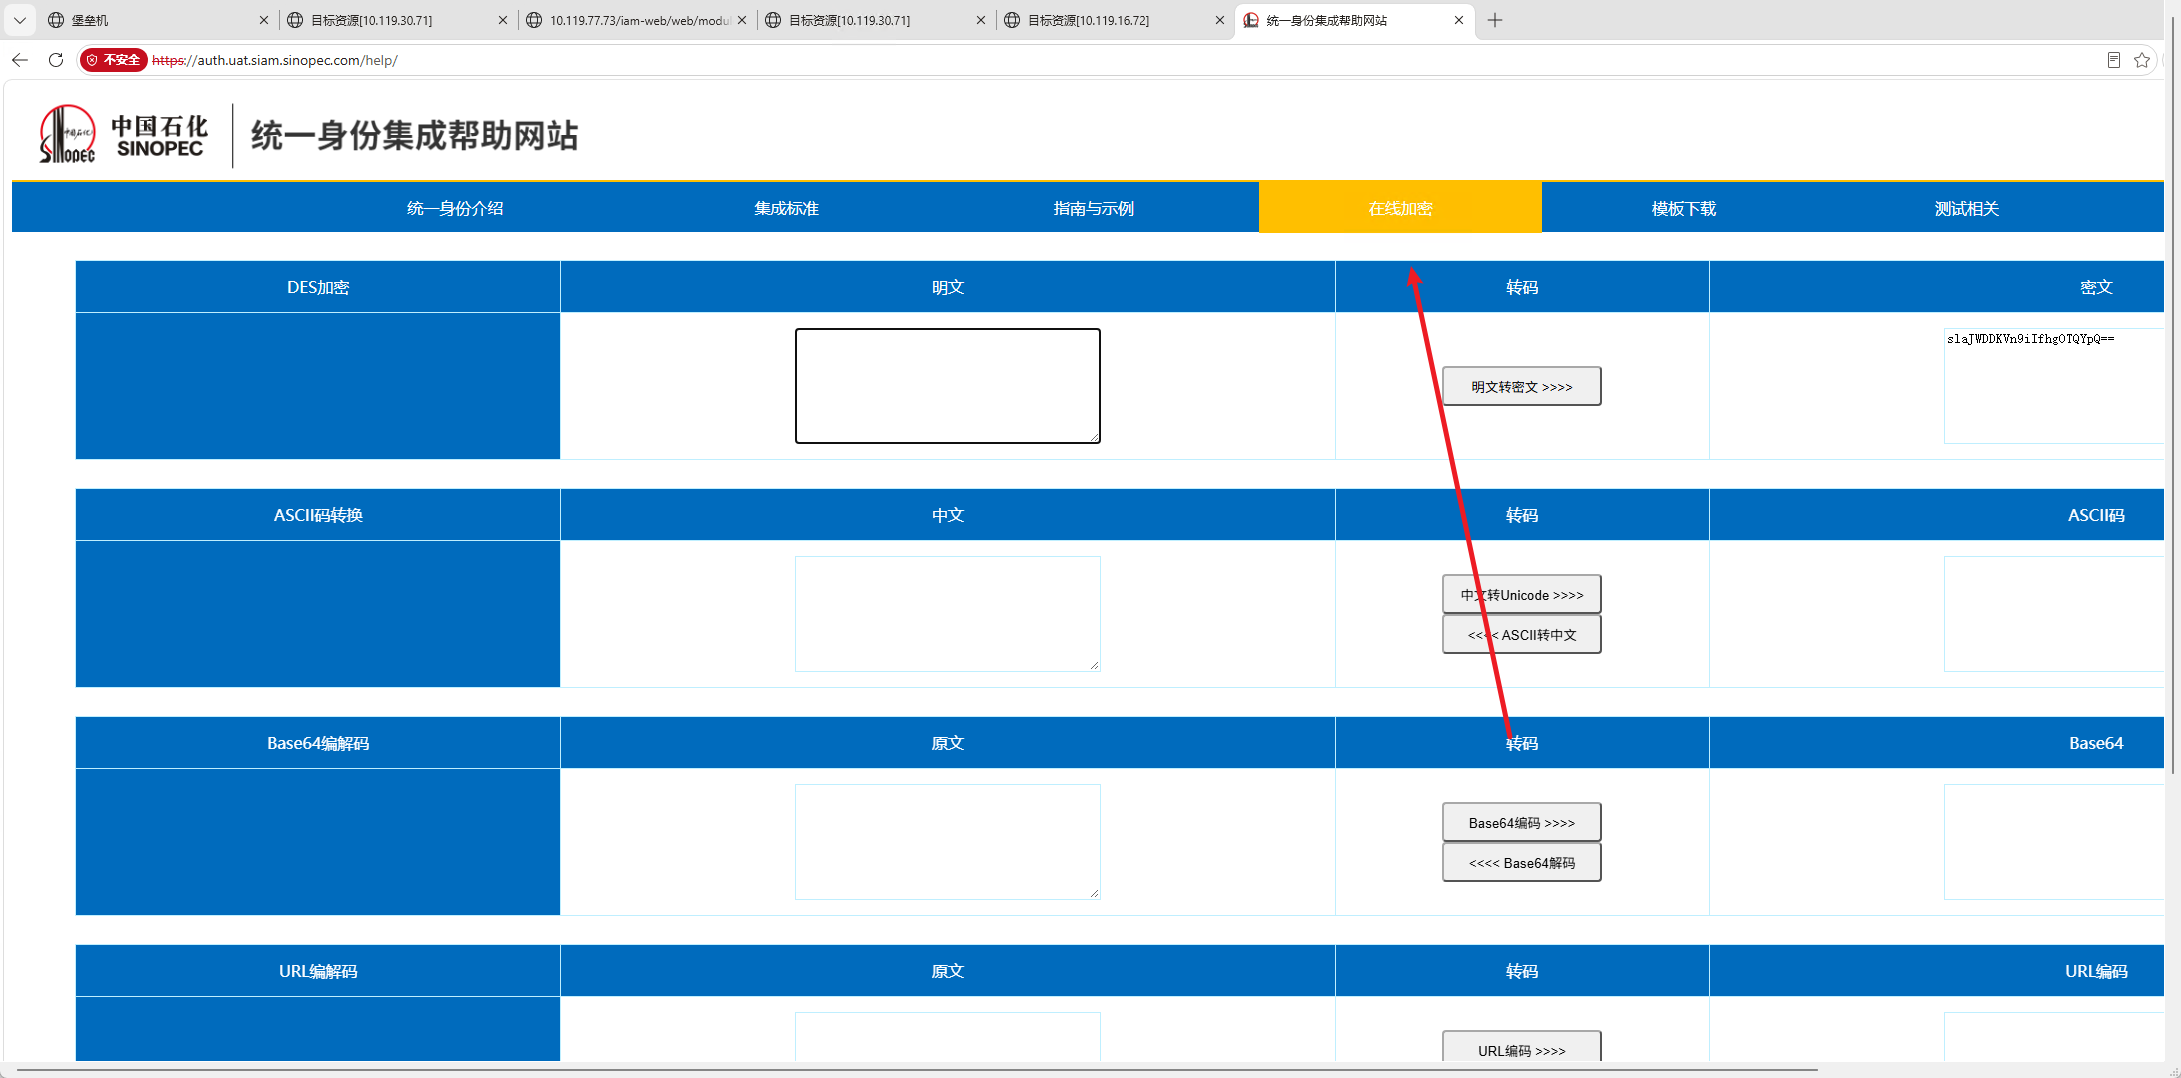
- 统一身份集成帮助网站: https://auth.uat.siam.sinopec.com/help/
- 加密也需要在帮助网站
前端的工作很简单:
js
bootstrapLogin() {
    const idpKey = this.$route.query && this.$route.query.idp_key;
    const forceLocal = this.$route.query && (this.$route.query.local === '1' || this.$route.query.local === 'true');

    // 1 带回 idp_key → 换 Token 登录
    if (idpKey) {
    this.loading = true;
    this.$store.dispatch("IdpLogin", idpKey).then(() => {
        this.$router.replace({ path: this.redirect || "/" }).catch(() => {});
    }).catch(() => {
        this.loading = false;
        this.$message.error("统一身份登录失败,请重试或使用本地账号登录");
        this.$router.replace({ path: "/login", query: { local: "1" } }).catch(() => {});
        this.showLocalLogin();
    });
    return;
    }

    // 2 强制本地登录
    if (forceLocal) {
    this.showLocalLogin();
    return;
    }

    // 3 无 idp_key:若开启 SSO 则跳统一身份
    getIdpConfig().then(res => {
    const data = res.data || res;
    if (data && data.authEnabled) {
        const loginUrl = data.loginUrl || "/idp/login";
        // 整页跳转到后端,由 AccessEnforcer 拉起统一身份
        window.location.href = process.env.VUE_APP_BASE_API + loginUrl;
    } else {
        this.showLocalLogin();
    }
    }).catch(() => {
    this.showLocalLogin();
    });
}
后端的工作
登录
- 集成jar包(企业内部仓库)
引用的jar包:
xml
<dependency>
    <groupId>com.sinopec.siam</groupId>
    <artifactId>siam-am-agent-simple</artifactId>
    <version>3.3.1</version>
</dependency>
<dependency>
    <groupId>com.sinopec.commons-pool2</groupId>
    <artifactId>commons-pool2</artifactId>
    <version>2.4.2</version>
</dependency>
仓库地址:
xml
<repositories>
    <repository>
        <id>public</id>
        <name>aliyun nexus</name>
        <url>https://maven.aliyun.com/repository/public</url>
        <releases>
            <enabled>true</enabled>
        </releases>
    </repository>
    <repository>
        <!-- LIMS 私服:含 SIAM 账号开通客户端 -->
        <id>nexus-lims</id>
        <name>nexus-lims</name>
        <url>http://192.168.0.57:8081/repository/maven-public/</url>
        <releases>
            <enabled>true</enabled>
            <updatePolicy>always</updatePolicy>
        </releases>
        <snapshots>
            <enabled>true</enabled>
            <updatePolicy>always</updatePolicy>
        </snapshots>
    </repository>
    <repository>
        <!--仓库id,这个id就是上面配置的账号密码id  -->
        <id>nexus</id>
        <!-- 仓库的名称 -->
        <name>nexus</name>
        <!--仓库的地址  -->
        <!--                        <url>http://123.56.245.155:9111/repository/maven-public/</url>-->
        <url>http://192.168.0.80:8081/repository/maven-public/</url>
        <!-- 是否开启该仓库的 release 版本下载支持 -->
        <releases>
            <enabled>true</enabled>
            <updatePolicy>always</updatePolicy>
        </releases>
        <!-- 是否开启该仓库的 snapshot 版本下载支持 -->
        <snapshots>
            <enabled>true</enabled>
            <updatePolicy>always</updatePolicy>
        </snapshots>
    </repository>
</repositories>
配置文件中添加idp-config的配置
yml
idp-config:
  authEnabled: false
  authRedisEnabled: false
  mqEnabled: false
  #在Java中使用response.sendRedirect时,总是默认使用部署的http协议,负载均衡使用的https协议,只能通过配置取主机头
  entityId: https://10.213.119.242/sysmanager
  jwt-auth:
    host: jwt.siam.sinopec.com
    singleFactorAuthurl: https://jwt2.uat.siam.sinopec.com/jwt2/jwtauth
    twoFactorAuthurl: https://jwt2.uat.siam.sinopec.com/jwtauth_userpwdotp
    authorization: Bearer
    content-type: application/x-www-form-urlencoded; charset=UTF-8
    #应用程序ID
    appId: 7624
    #应用连接账号ID
    account-name: sinopec_jwt_7624
    #应用密码
    account-pwd: sinopec_jwt_7624
MQ
1. mq的日志文件调整,不要与主应用的日志混在一起,不好排查问题
2. mq做成一个单独的服务
3. mq的证书在测试转生产的时候不需要换,只需要把生产的队列,密码等等更换掉就可以了
踩坑
1. 「分离式外置配置 + 外置 lib 依赖包」的 SpringBoot 打包 pom 配置
报错: unable write .............ruoyi-admin!
原因: 认证中心会往服务器的文件下写两个xml文件,如果打成一整个jar包,那么会导致认证中心写不进去。
xml
<build>
    <finalName>${project.artifactId}</finalName>
    <resources>
        <resource>
            <directory>src/main/resources</directory>
        </resource>
        <resource>
            <directory>src/main/java</directory>
            <includes>
                <include>**/*.xml</include>
            </includes>
            <excludes>
                <exclude>**/*.java</exclude>
            </excludes>
        </resource>
    </resources>
    <defaultGoal>install</defaultGoal>
    <plugins>
        <plugin>
            <groupId>org.springframework.boot</groupId>
            <artifactId>spring-boot-maven-plugin</artifactId>
            <configuration>
                <includeSystemScope>true</includeSystemScope>
            </configuration>
        </plugin>
        <plugin>
            <groupId>org.apache.maven.plugins</groupId>
            <artifactId>maven-jar-plugin</artifactId>
            <configuration>
                <!--这些配置将写入到MANIFEST.MF文件中-->
                <archive>
                    <!--指定程序入口-->
                    <manifest>
                        <addClasspath>true</addClasspath>
                        <classpathPrefix>lib/</classpathPrefix>
                        <mainClass>com.ruoyi.RuoYiApplication</mainClass>
                    </manifest>
                    <!-- (配置文件外置目录) -->
                    <manifestEntries>
                        <Class-Path>conf/</Class-Path>
                    </manifestEntries>
                </archive>
                <excludes>
                    <exclude>**/*.yml</exclude>
                    <exclude>**/*.xml</exclude>
                    <exclude>**/*.properties</exclude>
                </excludes>
            </configuration>
        </plugin>
        <plugin>
            <groupId>org.apache.maven.plugins</groupId>
            <artifactId>maven-dependency-plugin</artifactId>
            <executions>
                <execution>
                    <id>copy-lib</id>
                    <phase>prepare-package</phase>
                    <goals>
                        <goal>copy-dependencies</goal>
                    </goals>
                    <configuration>
                        <outputDirectory>${project.build.directory}/lib</outputDirectory>
                        <overWriteReleases>false</overWriteReleases>
                        <overWriteSnapshots>false</overWriteSnapshots>
                        <overWriteIfNewer>true</overWriteIfNewer>
                        <includeScope>runtime</includeScope>
                    </configuration>
                </execution>
            </executions>
        </plugin>
        <plugin>
            <groupId>org.apache.maven.plugins</groupId>
            <artifactId>maven-resources-plugin</artifactId>
            <executions>
                <execution>
                    <id>copy-config</id>
                    <phase>package</phase>
                    <goals>
                        <goal>copy-resources</goal>
                    </goals>
                    <configuration>
                        <outputDirectory>${project.build.directory}/conf</outputDirectory>
                        <resources>
                            <resource>
                                <directory>src/main/resources</directory>
                                <includes>
                                    <include>**/*.xml</include>
                                    <include>**/*.yml</include>
                                    <include>**/*.properties</include>
                                </includes>
                                <filtering>true</filtering>
                            </resource>
                        </resources>
                        <encoding>UTF-8</encoding>
                    </configuration>
                </execution>
            </executions>
        </plugin>

    </plugins>
</build>
2. 配置文件添加id-config:
yml
idp-config:
    authEnabled: true
    authRedisEnabled: true
    mqEnabled: false
    #在Java中使用response.sendRedirect时,总是默认使用部署的http协议,负载均衡使用的https协议,只能通过配置取主机头
    entityId: https://10.213.119.242/sysmanager
    frontendUrl: http://localhost:8800
    jwt-auth:
        host: jwt.siam.sinopec.com
        singleFactorAuthurl: https://jwt2.uat.siam.sinopec.com/jwt2/jwtauth
        twoFactorAuthurl: https://jwt2.uat.siam.sinopec.com/jwtauth_userpwdotp
        authorization: Bearer
        content-type: application/x-www-form-urlencoded; charset=UTF-8
        #应用程序ID
        appId: 7624
        #应用连接账号ID
        account-name: sinopec_jwt_7624
        #应用密码
        account-pwd: sinopec_jwt_7624
3.上线前修改日志文件目录,方便查看日志,避免找不到日志
4.nginx反向代理 /api_root 到业务后台
原因: 后续改生产环境的时候需要改成https,方便在nginx上配置https
5.数据库迁移
- 达梦管理工具的版本本机最好跟堡垒机上的保持一致,方便导入导出dmp文件
6. 认证中心的证书制作
- 要确认与认证中心注册的cer文件是否与生成jks文件的cer文件是否一致
使用以下的命令在堡垒机制作jks:
keytool -import -trustcacerts
-keystore /home/gzshgly/app/ssl/10.119.30.71.jks  //jks文件地址
-storepass 'Ski_123!@#' //证书密码
-alias 10.119.30.71  //别名
-file /home/gzshgly/app/ssl/10.119.30.71.cer   //cer文件地址
7. 测试环境改成测试环境的工作:
- 将所有的http改成https
- 认证中心证书的切换(jks/p12,java使用jks,其他语言使用p12)
- entityId修改
- 应用程序ID
- 应用连接账号ID
- 应用密码
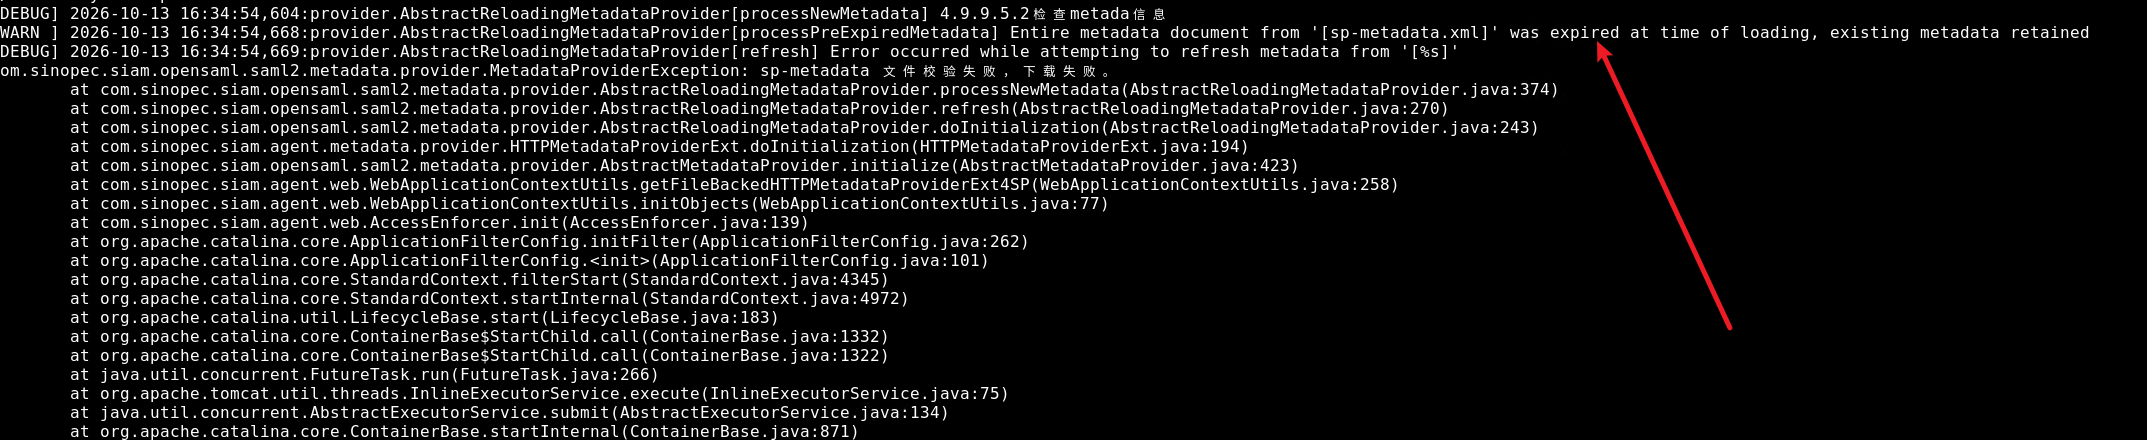
8. 如果meta文件报以下的错误,那就是jks文件的生成有问题
9. 认证中心官方生成jks
- 生成jks
keytool -genkeypair -alias 10.119.30.71 -keyalg RSA -keysize 2048 -keypass 'Ski_123!@#' -sigalg SHA256withRSA -dname "CN=10.119.30.71,L=广州,O=中国石化化工股份有限公司广州分公司,C=CN" -validity 5475 -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storetype JKS -storepass 'Ski_123!@#'- 导入一级根证书
keytool -import -trustcacerts -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storepass 'Ski_123!@#' -alias root -file /home/gzshgly/app/ssl/root.cer- 导入二级根证书
keytool -import -trustcacerts -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storepass 'Ski_123!@#' -alias issuer -file /home/gzshgly/app/ssl/issuer.cer- 导入业务证书
keytool -import -trustcacerts -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storepass 'Ski_123!@#' -alias 10.119.30.71 -file /home/gzshgly/app/ssl/10.119.30.71.cer10. openssl生成的证书:
- 生成p12证书:
openssl pkcs12 -export -in /home/gzshgly/app/ssl/10.119.30.71.cer -inkey /home/gzshgly/app/ssl/10.119.30.71.key -out /home/gzshgly/app/ssl/10.119.30.71.p12 -name 10.119.30.71- 将p12证书转为jks的证书
keytool -importkeystore -srckeystore /home/gzshgly/app/ssl/10.119.30.71.p12 -srcstoretype PKCS12 -srcstorepass 'Ski_123!@#' -destkeystore /home/gzshgly/app/ssl/10.119.30.71.jks -deststoretype JKS -deststorepass 'Ski_123!@#'- 导入一级根证书
keytool -import -trustcacerts -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storepass 'Ski_123!@#' -alias root -file /home/gzshgly/app/ssl/root.cer- 导入二级根证书
keytool -import -trustcacerts -keystore /home/gzshgly/app/ssl/10.119.30.71.jks -storepass 'Ski_123!@#' -alias issuer -file /home/gzshgly11. 认证中心登录完之后报错
修改认证中心的配置文件,将地址添加到后面就好了 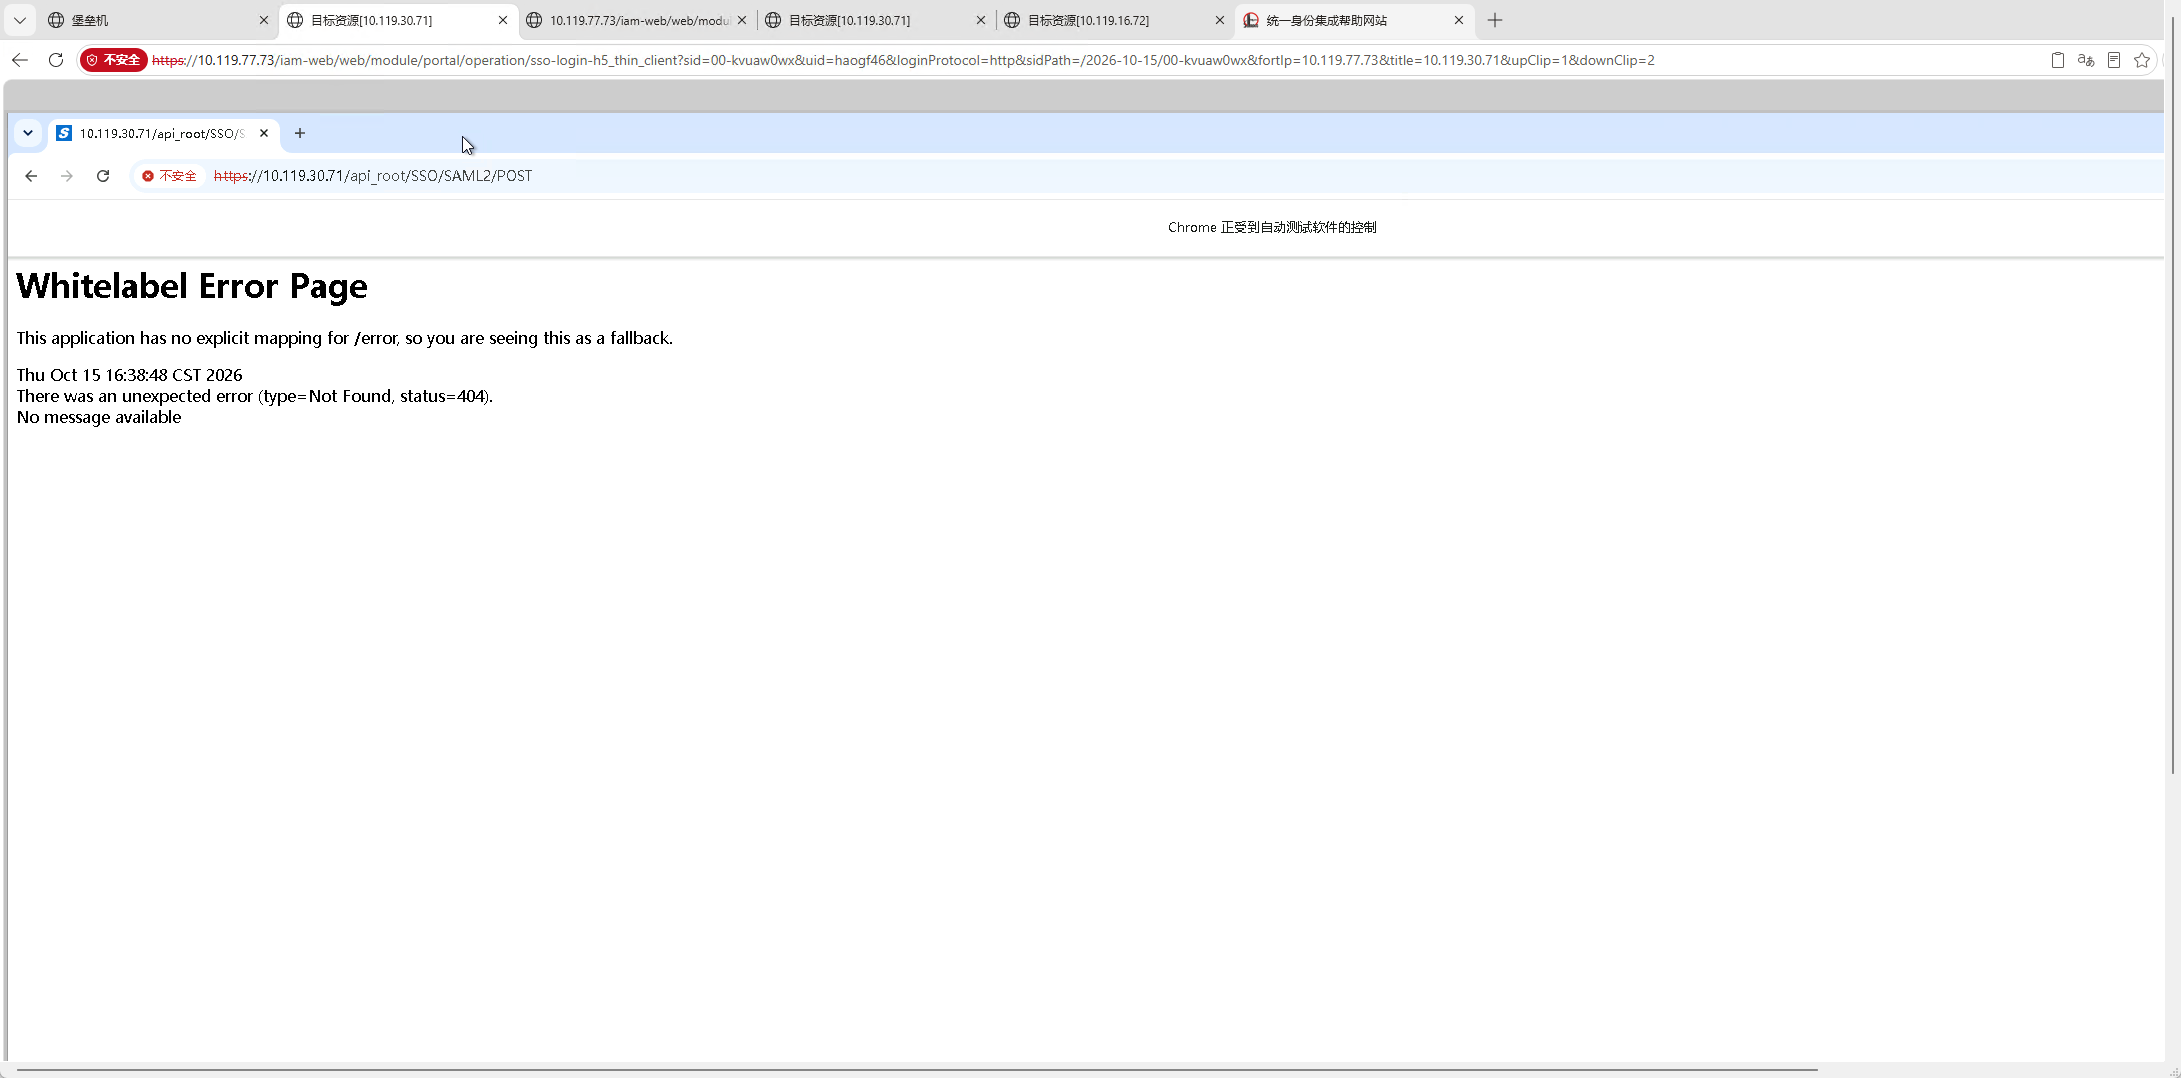
12. 生产初步可以使用之后,禁用TLS1.1后,退出报错
TSL协议介绍:传输层安全协议(TSL = Transport Layer Security),是SSL的继任者;HTTPS就是HTTP + TLS,跑在TCP之上
三大目标: 加密防窃听、证书身份校验、防篡改(完整性)
原因: TSL1.0和TSL1.1已经废弃了,TSL1.0存在BEAST、POODLE漏洞,等保/中石化禁用,TSL1.1弱加密套件(3DES、SHA1) 解决方案: 将前端的退出方法改为浏览器直接跳转访问,一定记得清除token。
js
LogOut({ commit, state }) {
    commit('SET_TOKEN', '')
    commit('SET_ROLES', [])
    commit('SET_PERMISSIONS', [])
    removeToken()
    window.location.href = `${window.origin}/prod-api/idp/loginOut`
}
13. 不要修改任何示例代码中的日志相关的代码
原因: 目前的示例代码是经过验证的,日志都是可以直接截图到测试报告上的,所以改完业务代码之后可以直接截图写测试报告了